Thryam

Machine identity automation.

Zero human intervention.

Prepare your infrastructure for 47-days TLS certificates with no-touch automation.

TLS lifespans are shrinking to
just 47 days in 2029

The CA/Browser Forum has ratified shorter TLS certificate lifespans. Manual renewal is becoming impossible. Automation isn't optional. It's survival.

2027

4 renewals

per certificate per year. Certificate validity drops to 100 days. 

2029

8 renewals

per certificate per year. Certificate validity drops to just 47 days. 

Workforce Calculator

Can your team keep up?

Certificate lifespans are shrinking to 47 days. See what that means for your team and what changes with Asparz.

Number of TLS Certificates

10,000

Hours per Renewal (manual)

4 hrs

Fully Loaded Cost per FTE

$110K /year

Without Automation

2027 (100-day certs)

—

—

2029 (47-day certs)

—

—

With Asparz

2027 (100-day certs)

—

—

2029 (47-day certs)

—

—

Annual savings by 2029 (before platform cost) —

CFO View

—
—
A single certificate outage costs an estimated $1.1M. Prevention is cheaper than recovery.

CISO View

—
Every manual renewal is a risk surface: misconfiguration, missed expiry, broken chain of trust.
With Asparz, your team oversees policy. The platform handles execution, logging, and discovery.
Introducing Asparz Video

Introducing Asparz

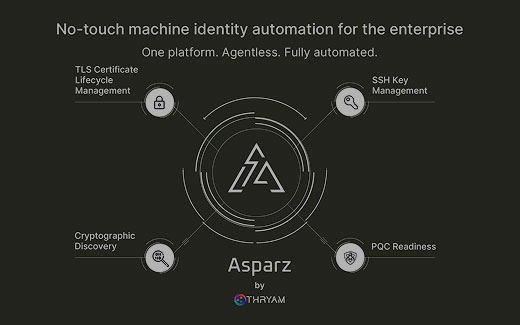
Asparz is a no-touch machine identity automation platform. It discovers, manages, and secures every machine identity across your infrastructure. TLS certificates, SSH keys, cryptographic assets, and PQC readiness. Your team oversees, the platform handles everything else.

No agents. No manual renewals. No missed expirations.
Free Asparz Discovery Tool

How many TLS certificates and SSH keys are you actually running?

Find known and unknown TLS certificates across your estate

Build a live inventory across endpoints, cloud, on-prem, Kubernetes, and load balancers

Identify forgotten SSH keys and machine identities across your environment

Surface expiring and misconfigured certificates before they become incidents

Prioritize what to fix first before any commitment

Get My Free Discovery Scan 

Gain immediate visibility into your TLS certificate and SSH key estate at no cost, no contracts, and no obligations.


    Your information stays with us. We never share it with third parties.

    Built different. On purpose.

    What makes Asparz different from the tools you've already looked at.

    Agentless

    No software to install on your endpoints. No infrastructure overhead to approve. No maintenance burden to absorb. Asparz works with your existing environment from day one.

    Audit-ready from day one

    Every action Asparz takes is logged and traceable. Your auditors get structured data, not screenshots and spreadsheets.

    Predictable pricing

    Your cost doesn't scale with your certificate count. Whether you have 1,000 or 100,000 certificates, the platform cost stays predictable.

    Single platform, not a patchwork

    TLS certificates, SSH keys, cryptographic assets, and PQC readiness in one place. No separate tools, no separate dashboards, no separate vendors.

    4 to 6 week implementation

    Not a 6-month deployment project. Asparz goes live in 4 to 6 weeks, including discovery, configuration, testing, and production cutover. Our founders are involved in every implementation.

    Endpoint-level depth

    Most competitors stop at network-level scanning. Asparz goes deeper. That depth is the difference between knowing what you have and knowing whether your infrastructure is actually ready.

    Four problems. One platform.

    Asparz automates and secures machine identities across your entire infrastructure. No-touch by design.

    TLS Certificate Lifecycle

    Certificates that discover, renew, and deploy themselves.

    Asparz discovers every certificate across your infrastructure. When renewal triggers, the platform handles it end to end. No human in the loop. Every step auditable.

    • Continuous discovery across your entire environment
    • Fully automated renewal and deployment
    • Works with your existing CA, CMDB, ITSM, and observability stack
    SSH Key Management

    Find every key. Eliminate the sprawl.

    SSH keys grant privileged access and never expire. They get created ad-hoc, shared across environments, and forgotten when people leave. Asparz gives you complete visibility and the context to act on it.

    • Full inventory across all endpoints
    • Identify orphaned, stale, and overshared credentials
    • Sprawl metrics tracked over time
    Cryptographic Discovery

    See everything. Secure what matters.

    You can't secure what you can't see. Asparz builds a complete cryptographic inventory across your infrastructure. The result is a compliance-ready bill of materials and a posture score your board can understand.

    • Comprehensive cryptographic bill of materials
    • Quantum readiness classification
    • Audit and compliance-ready reporting
    PQC Readiness

    Preparing for post-quantum. Before it's urgent.

    Most tools can tell you which certificates are quantum-vulnerable. Asparz goes further, assessing whether your infrastructure is actually ready for the transition. That requires depth that network scanning alone cannot provide.

    • Endpoint-level readiness assessment
    • Prioritized migration planning
    • Executive-ready reporting

    Your data. Your control.

    On-Premise

    Deploy on your infrastructure. Your data never leaves your environment. Virtual machine or container-based deployment. Full control over updates, access, and data residency.

    Hybrid

    Seamless control across your entire cloud and on-prem footprint. Cloud convenience with data residency control. Best of both for organizations with distributed infrastructure.

    Three steps. Six weeks.

    How to Get Started
    Step 01

    Demo

    We demo Asparz against your specific environment. Your infrastructure, your certificate inventory, your pain points. Not a generic walkthrough.

    Step 02

    Implementation

    A dedicated team walks you through a 4 to 6 week implementation. What we handle, what you handle. Full transparency.

    Step 03

    Go Live

    You transition from manual management to no-touch automation. Asparz discovers, monitors, procures, and deploys without human intervention.

    The real conversation starts here.

    FAQ

    In-house scripts work for simple scenarios but break at scale. They require ongoing maintenance, aren't audit-ready, and create single points of failure. Asparz is enterprise-grade, audit-compliant, and requires no ongoing maintenance.

    Asparz can migrate your existing certificates in 4 to 6 weeks. We handle the migration completely. No data loss, no service interruption. Most organizations see immediate ROI from reduced operational overhead.

    Yes. Asparz integrates with any CA, including internal PKI. If your organization runs its own certificate authority, Asparz manages renewal with the same completeness as any external CA.

    4 to 6 weeks for 95% of enterprises. This includes discovery, configuration, testing, and production cutover. Our founders are involved in every implementation.

    Pricing is based on your environment and scale, not on the number of certificates. Contact us and we'll walk you through it with a straightforward quote based on your reality.

    Asparz integrates with any CA (public or private), CMDB, ITSM, and observability platform. Plug-and-play, no custom development required.

    A comprehensive inventory of every cryptographic asset in your environment. Exportable in industry-standard formats. Designed for auditors, compliance teams, and executive reporting.

    PQC readiness assessment is targeted for Q4 2026. It will assess your infrastructure's readiness for the post-quantum transition. If you want early access, contact us.

    Book a demo. We run it against your specific environment so you see real results, not a slide deck. We're also offering early-access partnerships for organizations that want to shape the platform.